
A verifier-specific application can be used to terminate the consumer facet of the secondary communication channel. This software would want to take care of a secret (probably a key pair) that it uses to authenticate to the verifier in accepting or providing the key being exchanged. It should be noted that the authenticator just isn’t required to be a bodily separate system from that on which the authentication is going on. The requirement for separation applies to the communication channel, not the gadget. A cryptographic challenge can bind approval to a specific gadget, key, or transaction so the control resists replay and session substitution. A danger engine can slow or step-up entry, but it’s nonetheless making an inference, not establishing the same degree of proof.
Advancements And Open Challenges
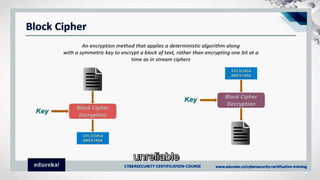
For some customers, they may be the easiest approach to check in — or the only practical method. ConvenienceThe usability of password substitute expertise must compete with the convenience of passwords, and one of many major usability advantages of passwords is that they can be used from any system. The word “passkey” is a standard noun; think of it the method in which you would check with “password”. Digital signatures are a typical instance — they confirm the sender’s identity and guarantee data hasn’t been tampered with.
- Wider deployment and real-world evaluation across domains stay ongoing, especially as privacy, scalability, and consumer experience are balanced in opposition to security in distributed, adversarial, and cell settings.
- This means the request essentially comes from a server that holds a legitimate TLS certificate for the corresponding domain, including a baseline layer of transport security before any passkey cryptography is involved.
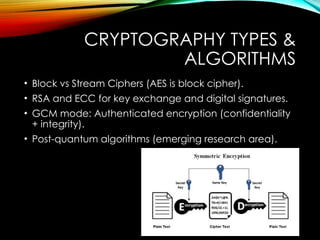
- It underpins every little thing from secure logins and online funds to e mail authentication and system integrity.
- Device-bound passkeys supply compliance with essentially the most stringent necessities throughout industries.
With cyberthreats on the rise and now centered on identity https://www.electionsscotland.info/5-takeaways-that-i-learned-about-4/, there is a need for methods of authentication that are resilient to phishing and human error. Builders ought to configure a customized domain in AuthKit before enabling passkeys in production, as credentials are sure to the area throughout registration. Altering the area later would orphan any passkeys created underneath the previous one. The browser still information the true origin in clientDataJSON, and the server should nonetheless confirm it against its record of anticipated origins. ROR simply extends the set of origins which might be permitted to make use of a given rpId, under the express control of the area proprietor. The trust anchor remains area control, verified by way of the well-known URI path.
Concern 1: Tips On How To Present Resistance To Mitm Phishing Assaults
Unlike conventional authentication systems that depend upon centralized servers to store and handle consumer credentials, DAPs utilize blockchain expertise, cryptographic methods, and distributed networks. This decentralized strategy enhances security, privacy, and person control over private data. Teleport points cryptographic identification to every participant involved in infrastructure entry, together with users, machines, bots, workloads, sources, and gadgets.
Cryptography Use Cases
If the user stores their passkeys on a FIDO Security Key, they’ll use it to securely authenticate on the new device and experience a portable root of trust across totally different units. Some need a credential that works throughout shared, restricted or unusual environments. A consumer may want hardware-bound protection for a checking account, e-mail account, GitHub account, crypto wallet, healthcare account or creator account.
For instance if a one-time password is used (such as from an OTP device), the attacker can use the authenticator output immediately after it is entered, so even a time-based OTP does not defend towards the attack. Challenge-response protocols are similarly ineffective because the attacker can open an authentication session and procure the challenge nonce, relay it to the claimant, after which have the required response to authenticate the attacker’s personal session. Apple, Google and Microsoft have carried out this answer, and are referring to synchronized key pair credentials as passkeys. However synchronization degrades security and person expertise by requiring customers to authenticate to the OS vendor with the same cumbersome and insecure MFA that FIDO purports to avoid.